
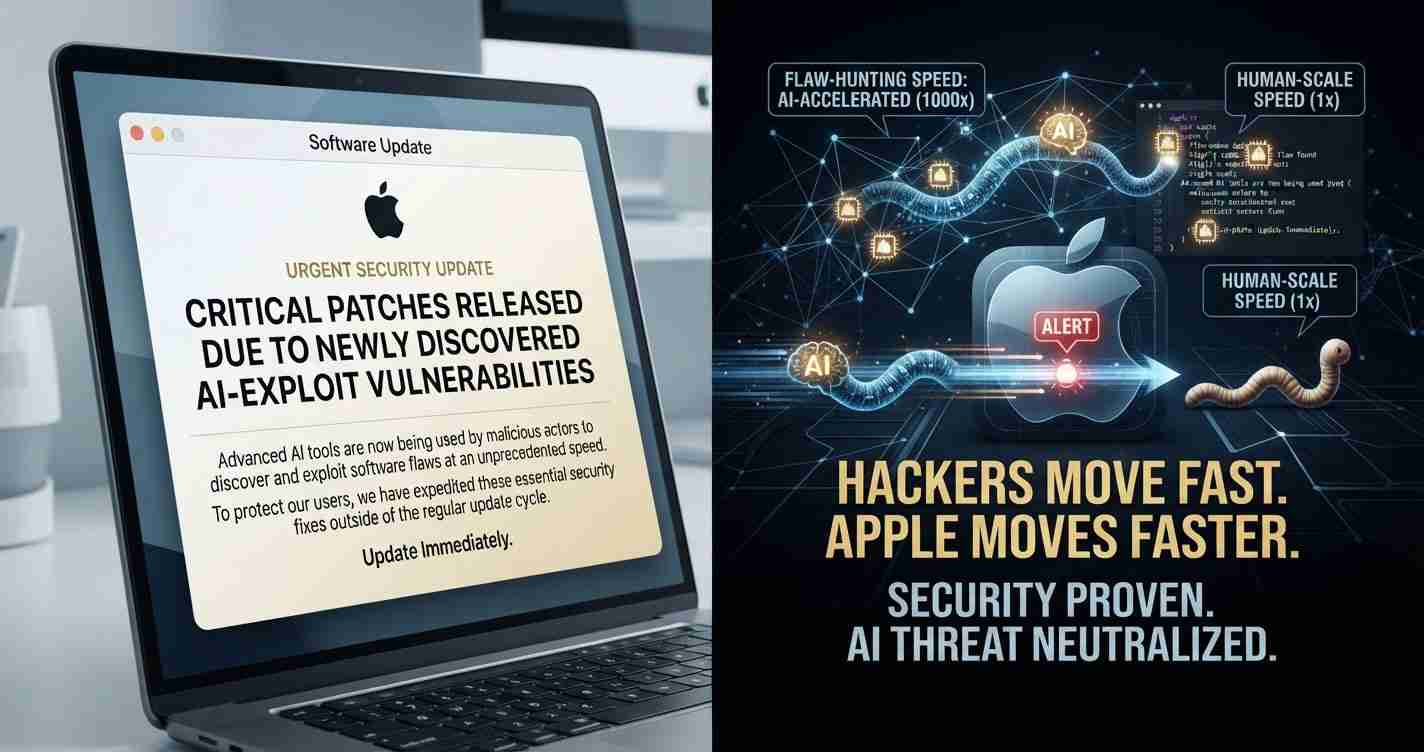
CUPERTINO, Calif., July 11 (San Francisco News Online) — Apple has started pushing some security fixes out earlier than planned for iPhone, iPad and Mac, saying the change is meant to close the gap between finding a flaw and getting the patch to users. In a statement reported by Reuters, Apple said it made the move because artificial intelligence can help attackers build malicious tools faster.
That matters because security updates are only useful if people get them before attackers can turn a weakness into a working exploit. Apple said there was no evidence the newly fixed problems had been used in attacks.
What changed
Apple normally folds many security fixes into larger software releases. Reuters reported that this time the company moved updates ahead of the next scheduled 26.6 release cycle. The June 29 release covered iOS 26.5.2, iPadOS 26.5.2 and macOS Tahoe 26.5.2.
Apple’s own release process appears to have changed in another way, too: Reuters reported that the fixes had first shown up in the iOS 26.6, iPadOS 26.6 and macOS Tahoe 26.6 beta builds before Apple sent them out early to all users.
Why Apple says it acted early
Apple told Reuters that AI is speeding up the creation of malicious hacking tools. In practical terms, that means security researchers, defenders and attackers can all move faster. When the time between a bug being discovered and a patch reaching devices gets shorter, there is less room for attackers to act first.
Quartz reported that the Five Eyes intelligence alliance has warned that frontier AI could sharply change both attack and defense in cybersecurity and shorten the time between finding a flaw and weaponizing it.
What the fixes covered
Coverage from Fox News and Quartz, based on Apple’s security update details, said the patches touched several important parts of Apple software, including the kernel, WebKit, WebRTC, libxslt and the IOGPUFamily graphics component.
Those terms matter because they sit near the center of how devices work:
- The kernel is the core part of an operating system. It manages memory, hardware and other low-level tasks.
- WebKit is the engine behind Safari and some app web views.
- WebRTC is used for real-time audio and video communication in browsers and apps.
Fox News reported that some of the flaws could have led to app crashes, memory corruption or leaks of sensitive kernel information. It also said WebKit problems could have caused crashes, memory corruption, data leaks or sandbox escapes, while WebRTC issues could have caused crashes.
Quartz reported that the update was available for iPhone 11 and later, along with several iPad lines.
What users should take from this
Apple’s move does not prove that a specific attack was underway. Apple said it had not seen evidence that the patched vulnerabilities were being exploited.
Instead, the release shows a shift in how Apple is handling security risk: it is not waiting as long to ship some fixes. That is important for users because the value of a patch depends on speed. The faster a fix reaches devices, the less time attackers have to use the flaw.
For consumers, the basic advice is unchanged: install security updates when they are available. For Apple, the broader lesson is that AI may be raising the pace of both bug hunting and exploitation, which can force companies to rethink how they ship patches.
